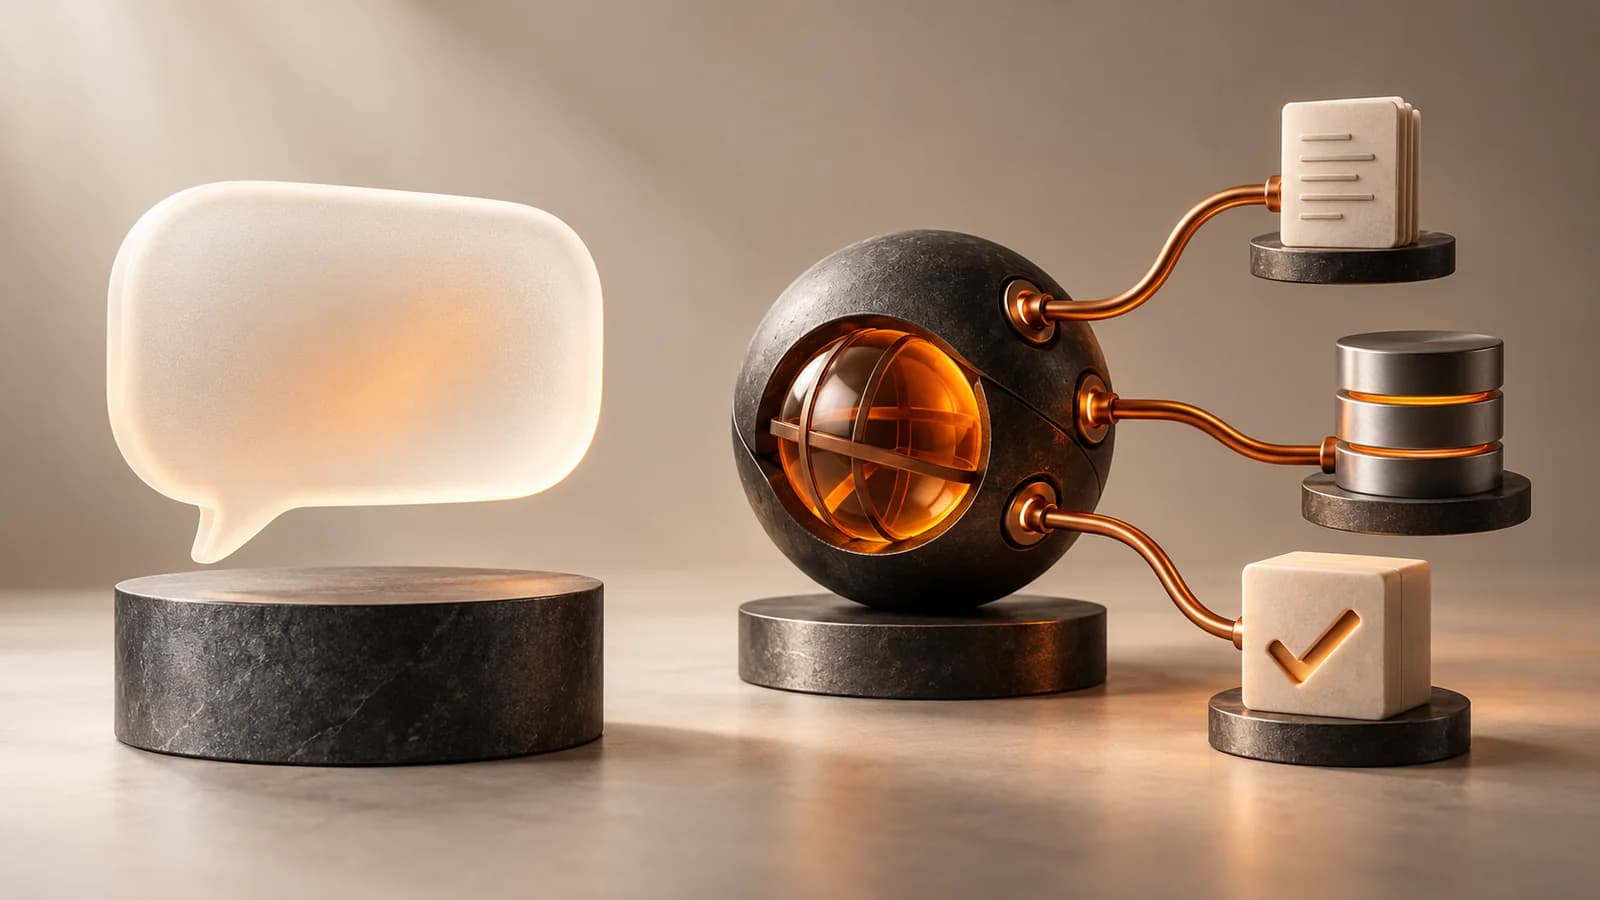
When someone asks software to find information, check it in another system and prepare a result, generating a paragraph is only part of the job. Something must connect the request to concrete operations. An AI agent can provide that connection: it is a software system that uses a model, relevant data and permitted tools to pursue a defined goal.
Imagine an internal support assistant. It needs to understand an employee’s question, find the current instructions and check the status of a request. This example helps explain the components of an agent, where the approach is useful and why developers must define its operating boundaries.
What makes a system an agent?
In a common architectural distinction, an agent can select its next step in response to information gathered during execution. It might search for a record and then decide whether the result requires a follow-up question. The sequence can vary between requests, while the goal, available tools and stopping conditions remain defined by the application.
A language model can interpret the request or propose an action. It is only one component. Application code checks permissions, connects to services and executes approved operations. Building an agent therefore involves more than writing instructions for a model: the surrounding software determines how those instructions become observable behavior.
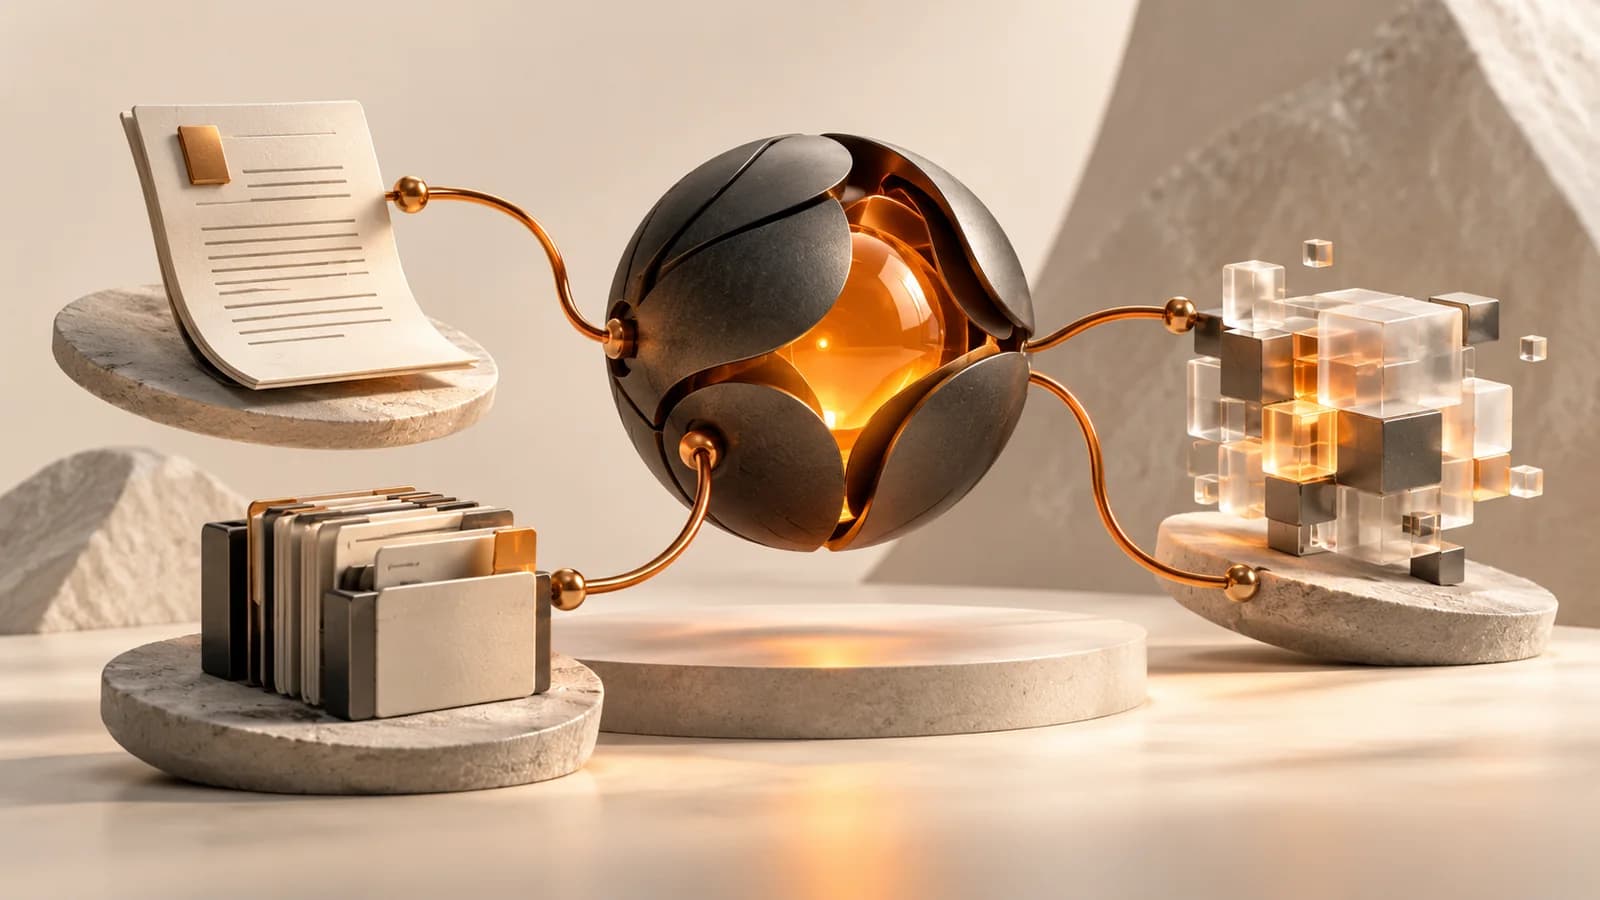
The components that work together
- A model. Processes the request and available context, then produces an answer or proposes the next step. Its output needs checks appropriate to the task.
- Instructions. Describe the role, response format, operating boundaries and situations that require a handoff to a person.
- Data sources. Documents, a knowledge base or business records that the requesting user is permitted to access.
- Tools. Specific software operations such as finding a request, reading a record, preparing a draft or creating a task.
- Execution state. Information about steps already taken and intermediate results within the current task.
- Execution controls. Argument validation, time and step limits, action logs and approval requirements for sensitive changes.
These components do not have to come from one vendor. The practical requirement is that they work together in a way the team can inspect, test and maintain. Adding more components is useful only when they solve a specific problem in the process.
A request, step by step
- An employee asks: “What is happening with my request for access to the system?”
- The application identifies the user and checks which requests they can view. It asks for a reference number if the request is ambiguous.
- The agent selects the permitted lookup tool. The server validates the arguments and performs the operation.
- The service returns the actual status. A missing record is treated as a distinct outcome rather than replaced with a plausible guess.
- The system explains the confirmed status, the record’s update time and the next available step.
- If resolving the request requires changing an assignee or access rights, the agent prepares a proposal for approval under the organization’s rules.
This sequence separates an intention from a completed action. The system should report success after receiving confirmation from the relevant service. A model’s decision to call a tool is not evidence that the requested change happened.
Where the approach can help
Agent logic can be useful when a task spans several sources and intermediate results affect what happens next. Examples include internal support, preparing a briefing from documents or reviewing a request against existing records. First describe the process without technology labels: what arrives, what the employee needs and how a correct result can be recognized.
A predictable operation may not need this flexibility. Validating a required field or sending a notification when a status changes can often be handled by conventional automation. A smaller solution may be easier to explain, operate and support. The article on agents and chatbots explores that choice in more detail.
What an agent does not guarantee
Connecting a model to tools does not make it infallible. The system may misunderstand an ambiguous request, receive outdated information or encounter an unavailable service. Each workflow needs an explicit response to missing data, unsuccessful operations and repeated attempts. Sometimes asking a person is the correct completion of the task.
Permissions also need deliberate design. Finding a document, drafting a reply and changing an important record have different consequences. Application code must enforce the relevant permissions. Text inside a retrieved document should not grant additional access or redefine the rules under which an operation is allowed.
A sensible first implementation
Choose one process with accessible examples and an observable outcome. Collect ordinary requests, difficult cases and situations where asking for clarification or declining to act is correct. Before development, agree how the team will assess correctness, completion time and the amount of manual revision needed.
Keep the first version small enough to review. A team can learn more from a narrowly scoped pilot with clear evidence than from a broad assistant whose successes are hard to distinguish from convincing wording. Expand the scope after the initial process works under realistic conditions.
A useful agent has a defined task, a result that can be checked and clear boundaries on its autonomy. Start by agreeing those three things.
The preparation guide turns these questions into a practical brief covering data, integrations and the first release.